
Credential rotation in PHP integrations means replacing a key, token, password, or certificate used to access an external service and retiring the previous one in a controlled manner. It is not simply a matter of changing a value in a configuration file: the application, its running processes, and the remote provider must be coordinated so the transition does not interrupt operations or unnecessarily extend the use of an old credential.
The goal is to verify that the new credential works across all consumers before revoking the old one, while maintaining a limited compatibility window and preparing a response to failures. The procedure must match the service’s capabilities: some providers allow two active keys at once; others require an immediate replacement, leaving less room for testing.
Why rotation requires coordination between the application and provider
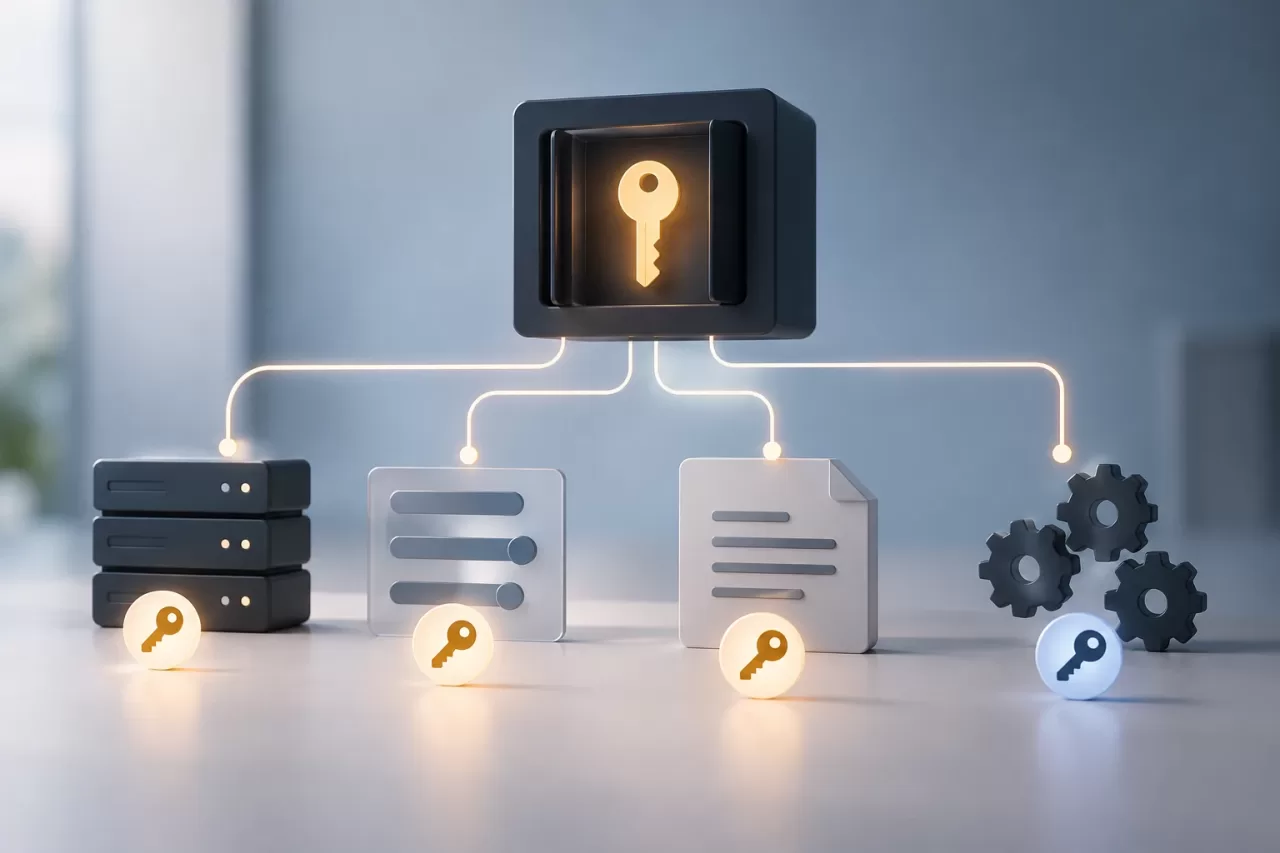
A credential often exists in several places at once: in the secrets manager, environment variables, deployment configuration, and PHP processes that have already started. Changing the value at its source does not guarantee that every consumer has reloaded it. For example, a long-running queue worker may retain an old configuration in memory while a web instance is already using the new one.
The behavior of the external system matters too. If it accepts old and new credentials simultaneously, you can deploy the new one, verify its use, and then revoke the old one. If it accepts only one, the operation may require a maintenance window, a coordinated sequence, or a change feature provided by the vendor. Do not assume overlap is available: confirm this in the documentation and, where possible, in a controlled environment.
Rotation differs from general configuration management. Configuration defines how a value is delivered and consumed; rotation changes the secret and its lifecycle, including validation, revocation, and response to exposure. Centralizing configuration helps, but does not by itself prove that the old credential is no longer being used.
Inventory consumers, permissions, and dependencies
Before generating or changing a credential, identify which service issues it, what permissions it grants, and every consumer that uses it. Include web applications, scheduled commands, workers, manual tasks, test environments, and operational tools. Also review repositories and CI/CD configurations for obsolete references, without copying the secret value into reports or tickets.
- Consumers: Identify repositories, services, processes, owners, and execution frequency.
- Scope: Document permissions, accessible resources, network restrictions, and any expiration date.
- Delivery: Confirm which manager or secure mechanism each process uses to obtain the credential and when it reads it again.
- Dependencies: Find out whether other systems or teams depend on the same key and whether the provider allows multiple active credentials.
- Observability: Locate metrics and success or error logs that let you verify the change without revealing sensitive values.
If you cannot determine who consumes a key, do not revoke it just because traffic appears low. A monthly process or recovery task can go unnoticed. Complete the inventory using the usage logs available from the provider and the effective configuration of the environments.
Prepare the transition and limit the overlap
Generate the new credential through the provider’s mechanism and grant it only the permissions it needs. If the service supports two active keys, set a defined overlap window that is long enough to deploy, test, and observe the consumers, but no longer than necessary. Recording who controls the window and what triggers revocation prevents the provisional period from becoming indefinite.
Deliver the secret through the approved system for the environment, not in source code, messages, tickets, or command-line arguments that may be logged. Avoid printing it in debug traces. To reduce errors, clearly distinguish references to the old and new credentials in procedures, but do not include their values in operational documentation.
Define the order of changes based on how configuration is loaded. You may need to update the secret, deploy the application, and restart workers or scheduled processes so they stop using values retained in memory. Confirm how changes propagate to each instance; a change in the runtime environment does not always update existing processes.
Deploy and verify without exposing secrets
Apply the change in a representative environment first, when the provider allows it. Then deploy in a coordinated manner to production and check both new calls and processes that may run less frequently. A basic connectivity test is useful, but it does not replace validation of the actual operations that depend on the integration.
- Verify that the application receives the new credential and that instances and workers have reloaded their configuration.
- Check provider responses, error codes, and business-relevant functional operations.
- Monitor success rates, authentication errors, retries, and pending queues for a period that covers the known consumers.
- Use request or execution identifiers to diagnose incidents; redact or exclude headers and bodies that could contain secrets.
Logs should provide context without storing tokens, passwords, or authorization headers. Review exception messages as well: a library or HTTP client may include sensitive data in a trace. If the integration processes personal or commercial information, also apply the relevant access, retention, and data-protection policies.
Revoke the old credential and respond to failures
Revoke the old key once all known consumers are working with the new one and observation has covered their relevant cycles. Confirm the revocation with the provider and monitor for subsequent errors. If attempts using the old credential continue to appear, look for forgotten processes, instances that have not been updated, or external tasks before considering the change complete.
When failures occur, distinguish authentication problems from permission, connectivity, or request-format problems. If the old credential is still active and there are no signs of exposure, it may serve as a temporary rollback while the deployment is corrected, provided there is authorization and a defined operational expiration. If the rotation is in response to suspected compromise, reactivating the old key may restore the risk: prioritize containment and follow the applicable security procedure.
Record decisions, times, owners, results, and outstanding actions, but never the secret. The record makes it possible to reconstruct what changed and helps repeat the process; it must not become a parallel inventory of credentials.
Checklist for repeatable rotation
- Have all consumers been identified, including long-running processes and infrequent tasks?
- Are the permissions, expiration, and provider rules for simultaneous credentials known?
- Is the new credential delivered through a secure channel and with least privilege?
- Does the plan specify the deployment order, configuration reload, observation period, and owner?
- Do the checks validate real operations and avoid logging sensitive values?
- Is there a distinct response for ordinary failures and possible compromises?
- Will the old credential be revoked, and will you check afterward that no consumers are still lagging behind?
A reliable rotation is complete when the new credential has been validated, the old one has been revoked, and no processes remain to be migrated. If any of these conditions cannot be verified, the change is still open and must be treated as an operational task with an explicitly assigned owner and follow-up.


