A useful administrative search feature is not about letting any user query any field in a table. It should help users complete specific operational tasks while respecting which records each role can view. In a PHP application, that distinction must be enforced on the server and applied to every route that returns information—not just to the back-office interface.
Designing secure search in a PHP back office requires agreement on what searching means, which criteria are allowed, how the access scope is calculated, and what limits protect the database. These criteria apply both to a straightforward SQL query and to a system based on a search index.
Start with tasks and access scope
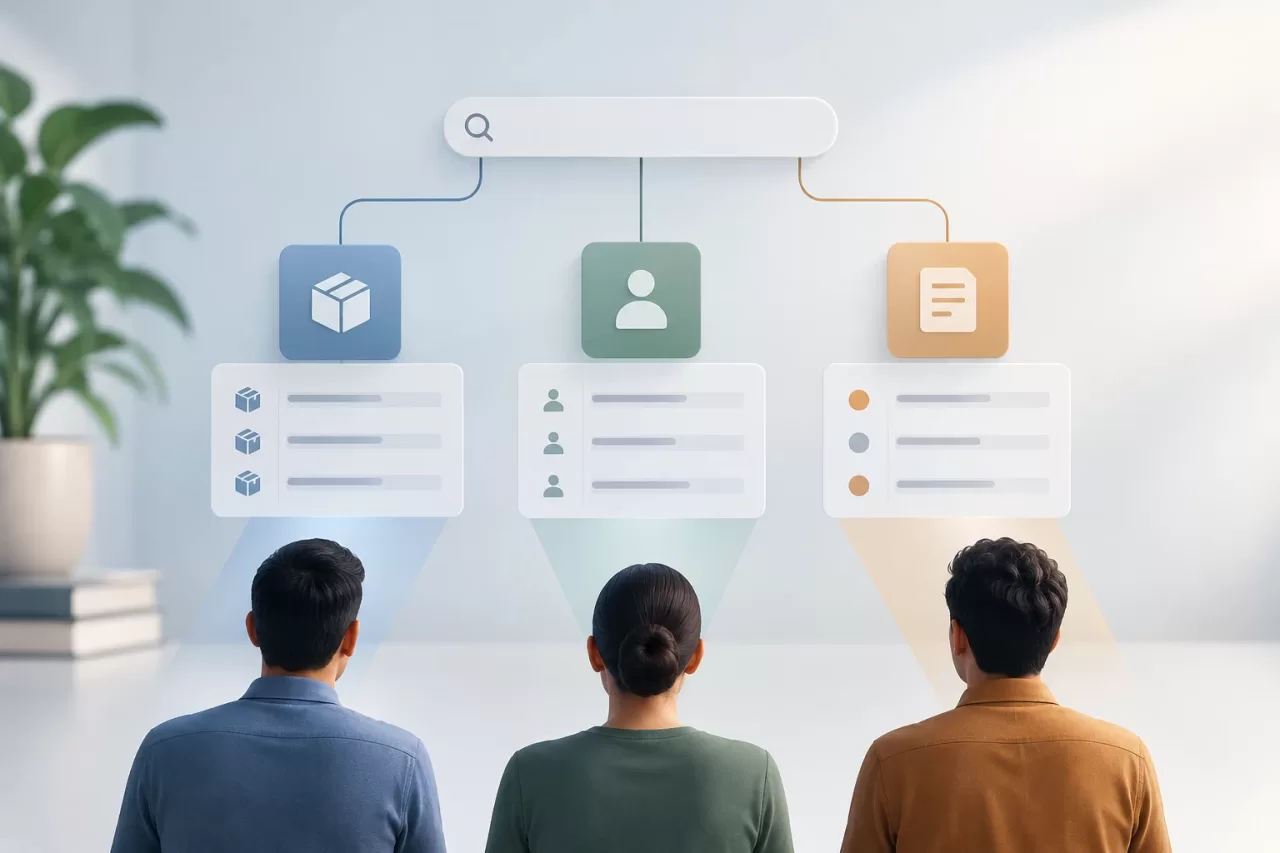
Before choosing fields or technology, identify which tasks search needs to support: locating an order by reference, finding an account by email, or reviewing incidents by status. For each task, note who performs it and which records they can query. Avoid defining the scope as “everything in the table”: a support agent, for example, might need access to certain customers, while an administrator might work with a different set.
Translate those rules into an understandable authorization model: by organization, team, owner, region, or another domain relationship. Also determine whether access can change over time and what happens when a user loses permissions while keeping a session open. The interface can hide options, but the effective rule must be checked on the server.
Define explicit filters and validate every criterion
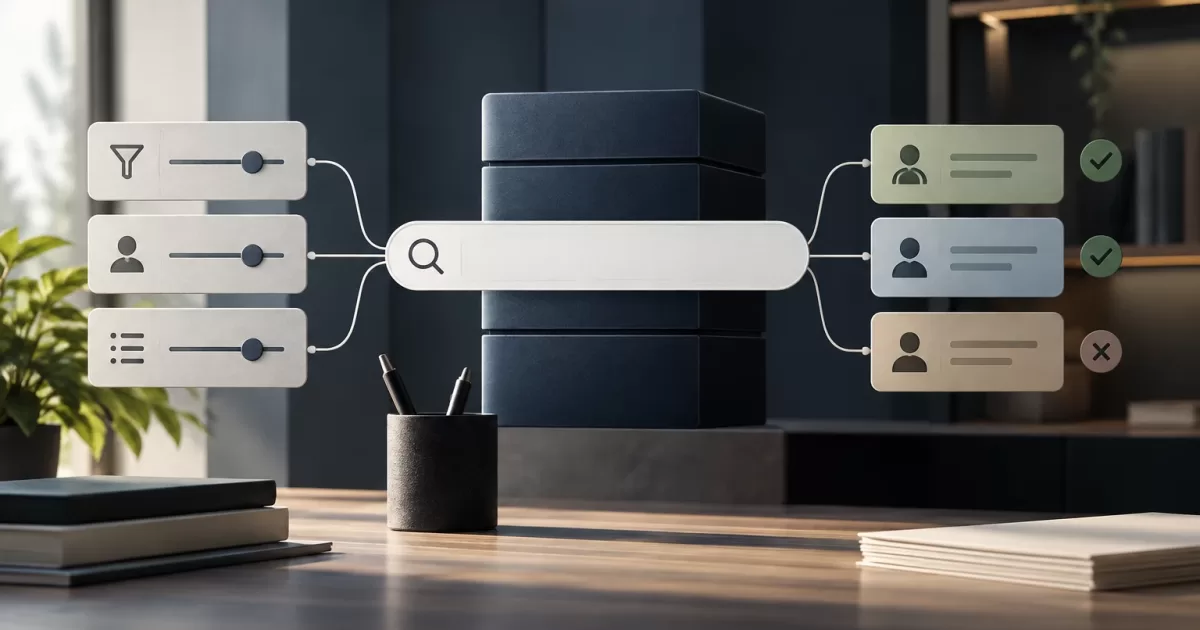
Design a limited list of searchable fields and filter types. For example, a screen might allow an exact reference, a status selected from a list, and a date range. Do not turn arbitrary parameters sent by the client into a column, SQL condition, or access criterion.
Validate values on the server: check formats, lengths, ranges, allowed values, and combinations. Use prepared statements to separate values from the SQL statement. Because prepared statements do not, by themselves, protect dynamic column names or sort orders, those elements must come from an allowlist defined on the server.
Business filters and authorization conditions are different things. A user can request “pending status,” but must not be able to send an organization ID to expand their scope. Calculate that scope using the authenticated identity and current rules, not by trusting editable form fields.
Apply authorization to rows, counts, and related actions
The access condition must be part of the query that retrieves results. Retrieving records first and filtering them afterward in PHP can expose data in logs, memory, responses, or auxiliary routes; it also complicates pagination and counting. Whenever possible, build the query so authorization conditions and search filters are applied together.
Review all associated outputs. A result total can reveal how many records exist outside the authorized scope; autocomplete suggestions can expose names or email addresses; an export might apply different rules from the screen. Links to detail pages and bulk actions must also respect the scope. Avoid response differences that make it possible to infer whether an inaccessible record exists when that information is also sensitive.
Centralize the construction of access criteria when doing so helps keep them consistent, but do not confuse a shared abstraction with automatic authorization: verify that each query and endpoint uses it correctly.
Choose between SQL and a search index
SQL is usually sufficient when filters are well defined, text relevance is not complex, and the database can resolve the query with suitable indexes. It is a direct option for combining equality conditions, ranges, relationships, and allowed sort orders. Review the execution plan and indexes before adding another component.
A search index can be useful if you need typo tolerance, linguistic analysis, text relevance, or searches across large volumes that SQL cannot handle within the required operational objectives. However, it adds synchronization, update delays, access control, and operational overhead. The index does not replace the database as the source of truth for permissions.
If the index contains data from multiple scopes, you must restrict the query by authorization before returning documents and consider how permission changes or revocations are propagated. For sensitive actions, validate access again against the source of truth. Define how much delay is acceptable and what happens if the index is stale or unavailable; one fallback may be to temporarily disable advanced search, not to bypass controls.
Limit cost, sorting, and response volume
Set a maximum page size and use stable pagination. For large datasets or results that change frequently, cursor-based pagination can avoid some of the problems caused by offset pagination, although it requires consistent sorting and clearly defined continuation criteria.
Allow sorting only by intended fields, and set a deterministic secondary sort, such as a unique identifier. Limit the length of text queries, date ranges, and number of filters; avoid empty searches that trigger expensive scans. For heavy operations, consider rate limits and maximum execution times. Search should not return fields the screen does not need.
Test permissions and edge cases
Include positive and negative tests for different roles and scopes. Verify that each user can find permitted records and cannot retrieve others by changing filters, paginating, sorting, or requesting a detail page. Add cases for combined filters, invalid values, empty results, and records whose owner or scope has changed.
Also test counts, suggestions, exports, and bulk actions. A useful test verifies not only that another user’s record does not appear in the list, but also that it cannot be found by an exact reference or inferred through an auxiliary response. When permissions change, verify that behavior updates according to the defined policy.
Operational metrics should help with diagnosis without creating another exposure. Log latency, errors, result volume, and operation type, while avoiding the storage of sensitive search terms or unnecessary personal data. Restrict access to these logs and define their retention period. Monitor slow queries and index errors separately to distinguish performance issues from authorization failures.
Checklist before releasing changes
- Tasks, roles, and access scopes are documented.
- Searchable fields, filters, sort orders, and limits are explicit.
- The server validates parameters and does not use client data to grant access.
- Authorization is applied to results, counts, suggestions, details, and exports.
- SQL or the index has a performance strategy and a fallback for failures.
- Tests cover permitted and denied access, permission changes, and combined filters.
- Logs and metrics support diagnosis without retaining unnecessary sensitive terms.
An administrative search feature is ready when it supports the intended tasks with understandable results, controlled costs, and verifiable access boundaries. If a relevance improvement requires expanding the data that can be queried or introducing an index, evaluate that change as part of the security model, not as an implementation detail.