When an assistant responds with information about another person or company, the problem is not just one of quality: it may be a privacy and access control violation. In a multi-user PHP application, conversational memory must be treated as data with a defined owner, scope, and lifecycle. Simply saving messages and retrieving them by a session identifier is not enough.
Conversational context isolation in PHP applications means ensuring that the material used to generate a response belongs to the current conversation and is still authorized. This includes previous messages, summaries, and any retrieved data. Document search can supplement the context, but it has different access rules and objectives.
Separate conversational memory, history, and documents
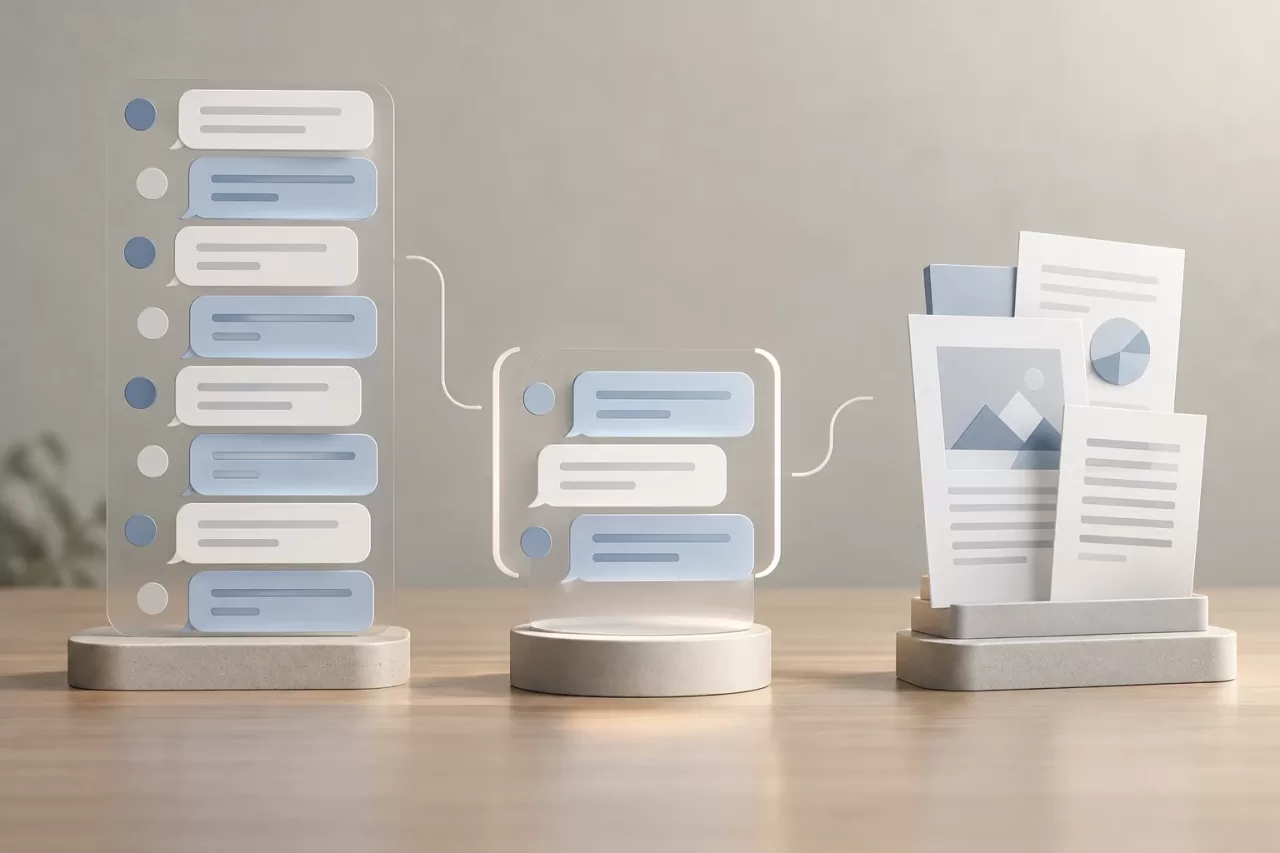
The complete history is the record of messages in a conversation. Memory, by contrast, is the subset the application chooses to retrieve for a task—for example, the latest turns or an updated summary. Documents retrieved through search are another source, selected based on a query and document permissions. They should not be confused with messages or stored as if they were messages spoken by the user.
This distinction makes it easier to make verifiable decisions. History can be retained for auditing or product reasons while limiting the memory sent to the model. Likewise, each document excerpt can retain its own source and access control. If these sources are mixed without being identified, it becomes difficult to explain which data influenced a response and apply its retention policy.
Define who owns each conversation
Before designing retrieval, establish a stable identity for the conversation. At a minimum, consider:
- Conversation: a random or unpredictable identifier, without assuming that knowing it grants access.
- User: the authenticated identity that initiated the interaction or has permission to access it.
- Organization: the data scope to which it belongs, if the application operates across multiple companies or workspaces.
- Current permissions: authorization evaluated at the time of each read, not an indefinite copy of the initial permissions.
The web session can be used to authenticate a request, but it should not be the only persistent ownership key. A person may log out, change organizations, or lose a permission while a conversation remains stored. For each request, the application must check that the current user can access that conversation within the active organization.
It is useful to explicitly define context changes. If someone changes organizations, can they continue the previous conversation, must they start a new one, or can they retain only an approved summary? There is no universal answer: it depends on the product and its privacy requirements. The decision should be reflected in verifiable rules, not an implicit assumption in the interface.
Apply the access scope before retrieving context
Authorization must be part of the query that retrieves the data, before it is added to the prompt. Retrieving a broad collection first and filtering it later in PHP increases the risk that an error, an alternate path, or a debug log will expose someone else’s content.
In a relational database, the query can include the conversation identifier, user, and authorized organization at the same time. For example, conceptually:
SELECT message_id, role, content, created_at
FROM conversation_messages
WHERE conversation_id = :conversation_id
  AND organization_id = :organization_id
  AND conversation_id IN (
      SELECT conversation_id
      FROM conversations
      WHERE owner_user_id = :user_id
         OR EXISTS (/* check for a current grant */)
  )
ORDER BY created_at DESC
LIMIT :message_limit
The actual schema may differ, but the important property is that the access scope constrains the records retrieved. Use bound parameters and a consistent authorization layer for read, write, export, and delete operations. If a vector database or search service is used, organization and permission constraints must be applied in the retrieval query; it is not enough to ask the model to ignore unauthorized results.
When document search and conversational memory are combined, apply the relevant authorization to each source first. Preserve provenance metadata and avoid turning document results into permanent memory without an explicit policy.
Prevent cross-context data leakage in caches, queues, and shared components
Correct database access does not guarantee isolation if other layers share state. A cache key such as conversation:123 may be insufficient if the same identifier is used in more than one scope, is reused, or a cache configuration allows collisions. Include organization and conversation identifiers in the key and, where appropriate, a permissions or data version. Do not use sensitive content as part of the key.
For background jobs, pass a minimal, explicit context: organization, conversation, actor, and job purpose. When the job runs, revalidate that it is still authorized and is not using an identity taken from shared global state. Avoid static variables, singleton services with mutable user data, and session objects reused across requests, especially in persistent PHP processes.
Also define what happens with errors and retries. A retried job should not switch organizations because of another process’s state, and a cached response should not survive a revocation if the policy requires it to be invalidated. The behavior should be deliberate and observable.
Limit memory to what the task requires
Isolation does not mean sending the entire history to the model. Retrieve recent turns or a summary that adds value to the current request, with limits on quantity and size. Consider freshness: old preferences, corrected data, and revoked decisions should not automatically be treated as current facts.
If summaries are used, store their scope and provenance, and update them according to clear rules. A summary is not a source of truth and does not replace permission checks. For critical data, consult the authorized system of record rather than relying on a statement saved in a previous conversation. A small context window reduces exposure and cost, but it does not compensate for incorrect authorization.
Test that one conversation does not influence another
Tests should cover both permitted and denied access. Create cases with different users and organizations and verify that a request does not retrieve messages, summaries, or documents from another identity. Include edge cases:
- A user changes organizations and reopens an old conversation identifier.
- A permission is revoked after the conversation is created but before its memory is retrieved.
- Two users make requests simultaneously and share processes, cache, or queue infrastructure.
- A nonexistent or unauthorized identifier produces a controlled response without revealing whether it belongs to someone else.
- A job is retried after a change in permissions or organization.
In addition to unit tests, test the full path from the authenticated request to context construction. You can insert marker messages into separate conversations and verify that the retrieved result for each one never contains the other conversation’s marker. The goal is to test the data boundary, not to evaluate whether the model writes a convincing response.
Investigate incidents without logging sensitive content
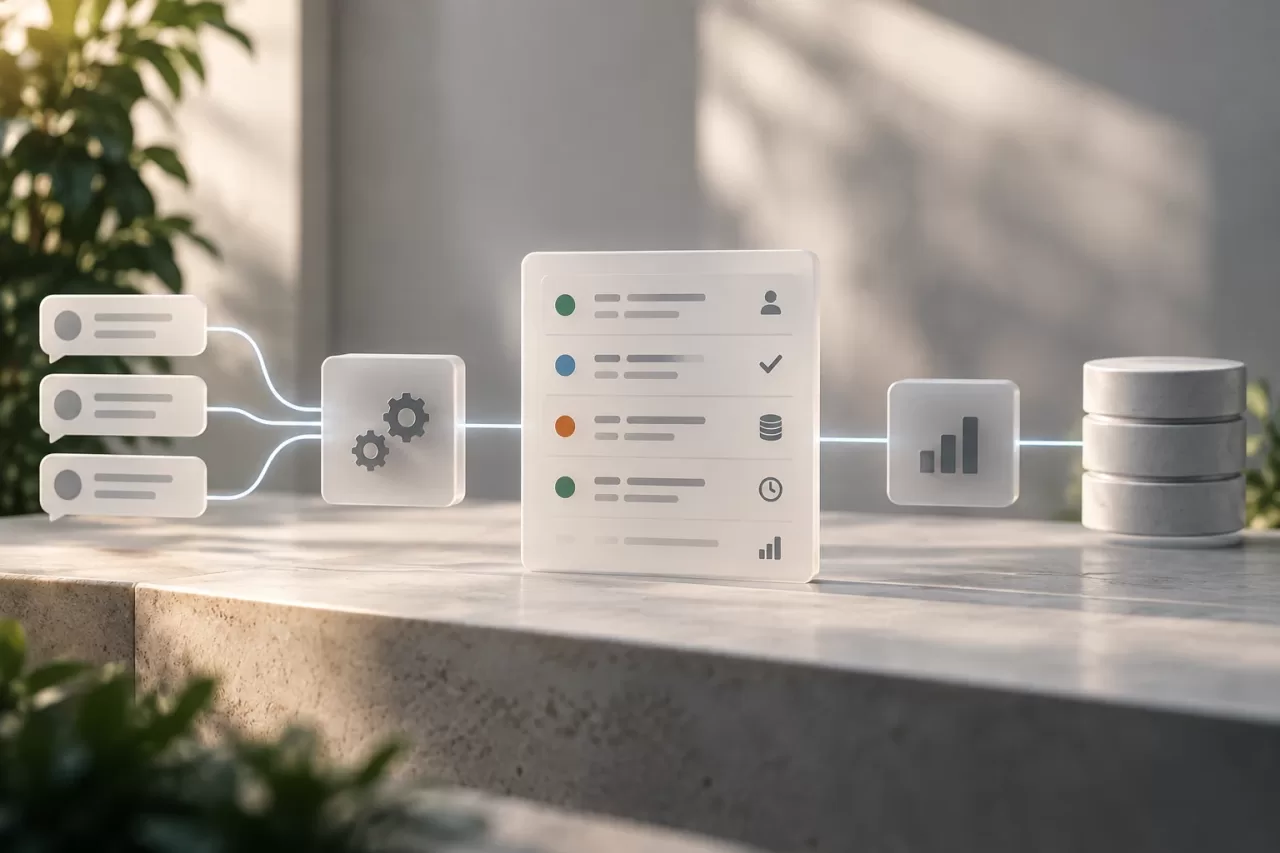
Observability should make it possible to trace the flow without copying private messages into logs. Record appropriate technical identifiers, authorization decisions, the number of items retrieved, data sources, duration, and the result of each stage. Use pseudonymous identifiers where possible, and restrict log access and retention.
Signals such as an unexpectedly empty retrieval, a mismatched organization, an unusual rate of denials, or a cache key reused outside its scope can help detect failures. Avoid logging complete prompts, documents, or responses by default. If detailed diagnostics are needed, establish a temporary, authorized, and limited procedure that redacts sensitive data.
A secure design makes the owner, scope, and freshness of each context fragment explicit. Applying those rules in queries, caches, and asynchronous jobs, and verifying negative cases, makes isolation a verifiable property of the PHP application—not an expectation placed on the assistant.