In a PHP project, a new request can seem small: adding a field, allowing an exception, or connecting a service. However, the visible coding effort does not always reflect the full impact. A modification can affect business rules, existing data, integrations, tests, and operational tasks. If it is accepted without reviewing those consequences, the team may lose predictability and deliver something different from what was agreed.
Managing scope changes in PHP projects is not about rejecting requests or preventing the product from evolving. It is about making explicit what is changing, why it matters, and what decision is being made. This allows business and technology stakeholders to compare alternatives using the same information, rather than renegotiating every request on an ad hoc basis.
First: Is It a Clarification, a Defect, or a Change?
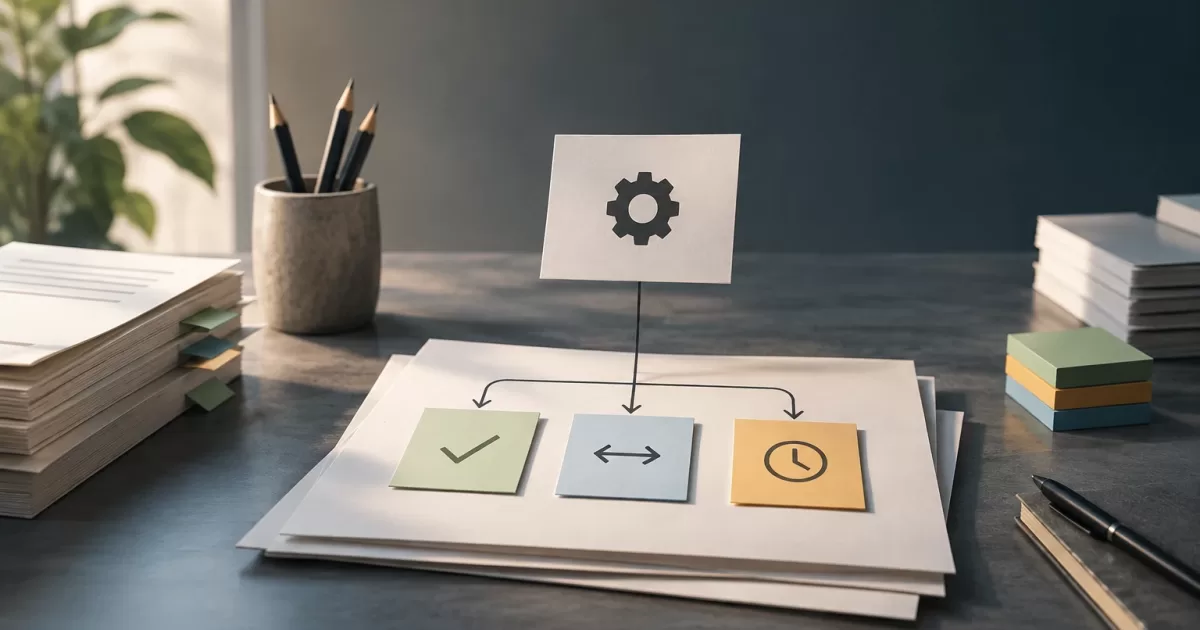
Before estimating, classify the request against the agreed scope and acceptance criteria. These categories are not interchangeable: each calls for a different conversation and a different way of handling it.
- Clarification: specifies how something already included should work, without changing the expected outcome. For example, confirming the date format that a previously specified screen should display.
- Defect: the product does not meet an agreed behavior or has a reproducible failure. Fixing it should not automatically be described as a scope enhancement.
- Scope change: modifies the expected behavior, adds a capability, or changes a condition that was not part of the agreement. For example, adding a new role with its own permissions when only an administrator role had been planned.
The distinction requires consulting requirements, examples, recorded decisions, and acceptance criteria; it is not enough for someone to remember the conversation differently. If the agreement is ambiguous, the first step is to clarify the shared baseline and document the interpretation. Avoid labeling a request a defect or a change to win an argument: record the evidence and resolve the classification with the people responsible.
Record the Problem Before Proposing a Solution
A useful request describes the need, not just the solution someone has in mind. “Add a CSV export” is a proposal; the underlying need may be for a team to reconcile orders with another system. This distinction makes it possible to compare options: exporting a file, providing a filterable report, or adjusting an existing integration may have different consequences.
At a minimum, record who needs the change, what problem they are trying to solve, who it affects, when it is needed, and how resolution would be verified. Add usage examples or edge cases if they help clarify the behavior. Also note which existing acceptance criteria would change and which new criteria would need to be agreed on.
In a PHP product, avoid assuming technical details before understanding the need. A new field, for example, raises questions about whether it is required, validation, historical data, permissions, search, reporting, and API compatibility. Not all of these will apply, but they are evaluation questions—not work that should be discovered after the request is approved.
Assess the Impact Beyond Coding Hours
An implementation estimate is only one part of the decision. Review the full path of the change and the dependencies it could affect:
- Business rules: Does it change a condition, exception, authorization, or amount calculation? Are there conflicting rules across teams or screens?
- Data: Are new columns, constraints, migrations, or changes to existing data required? What happens to old records and in the event of a rollback?
- Integrations: Does it affect API contracts, formats, asynchronous processes, external services, or consumers that rely on the current behavior?
- Testing: Which unit, integration, acceptance, or regression tests need to be expanded? Are there edge cases or permissions that need to be verified?
- Dependencies and delivery: Does it block other work, alter a deployment sequence, or require coordinating changes across more than one component?
- Operations and security: Does it add monitoring, support, configuration, personal data handling, or access controls that need to be maintained?
Separating uncertainty from effort improves the conversation. If it is not yet clear how to answer a technical or business question, specify what investigation is needed and what decision it will inform. Do not turn a preliminary estimate into a committed date without stating assumptions and dependencies.
Present Comparable Options
Once the impact has been identified, present alternatives that make the consequences clear. Not every request has to be accepted immediately or rejected outright.
- Incorporate: add the change to the agreed work and adjust scope, capacity, cost, or schedule as appropriate. This is suitable when the value justifies changing the plan and the dependencies are acceptable.
- Trade off: incorporate the request in exchange for removing or reducing other planned work. This can preserve a delivery constraint if both parties clearly agree on what will no longer be done.
- Split: deliver a useful part first and defer secondary elements. Define boundaries so the first part is not mistaken for the complete outcome and no risks are left without an owner.
- Defer: record the request for a later decision, with a condition or review date. Deferring does not mean losing it: preserve the reason for the request and prevent it from reappearing as a surprise.
Compare each option by expected value, effort, risk, dependencies, schedule impact, and operational cost. When information is missing, you can propose a bounded investigation before deciding on development. State the assumptions behind each option and what could change the recommendation; this avoids presenting a single technical answer as though it were the only business choice.
Agree on Who Decides and Update the Plan
Define in advance who can approve changes and who should contribute to the assessment. The person responsible for the product can prioritize value; the technical team identifies impacts and risks; business, security, or operations can validate the aspects that fall within their remit. One person must be accountable for the final decision; it should not be left implicit in a group conversation.
Document the request, its classification, the options considered, the decision, the reasons, the assumptions, and the accepted consequences. If the change is incorporated, update the delivery plan and acceptance criteria. If it is deferred, record when or under what condition it will be reviewed. If work is traded off, specify exactly what is removed or reduced. Maintain traceability in the work management system the team already uses; duplicating records without an owner often creates conflicting versions.
When closing the change, verify that the approved behavior is present in the product and that tests cover the agreed criteria. Update any technical or functional documentation that is now out of date, and communicate any outstanding limitations. Approving a request is not the same as delivering it: these are distinct statuses, and it is useful to make that difference visible.
A Short Template and Signs That a Broader Review Is Needed
A concise form helps assess requests consistently:
- Request and date: brief description and requester.
- Need: problem, affected users, and expected outcome.
- Classification: clarification, defect, or change, with a reference to the applicable agreement.
- Scope affected: criteria that change, rules, data, integrations, and operations.
- Options: incorporate, trade off, split, or defer; include assumptions and dependencies.
- Decision: owner, rationale, and consequences for the plan.
- Verification: acceptance criteria, tests, and documentation to update.
An isolated request can be handled with this process. However, it is worth reviewing the overall scope when requests accumulate, acceptance criteria change repeatedly, dependencies are unclear, or decisions displace work without updating the plan. It is also a warning sign when several small requests are found late to affect the same business rule or data model.
In these cases, estimating each request separately is not enough: review the project’s goals, priorities, capacity, and risks as a whole. Explicit change management makes it possible to change direction when there is a valid reason, while making trade-offs visible and protecting the quality of the PHP product being built.