Consumption limits in PHP APIs protect service availability and cost, but a poorly designed policy can disrupt legitimate integrations. Getting them right takes more than setting a number of requests per minute: you need to identify who is consuming resources, which operation they are performing, which resource is at risk, and how real traffic behaves.
An effective design combines limits suited to usage patterns, counters that stay consistent across instances, and responses that help consumers recover. It also requires observing the effect of the rules before tightening them, especially when multiple clients share credentials or depend on common resources.
Distinguish rate limits, quotas, and concurrency
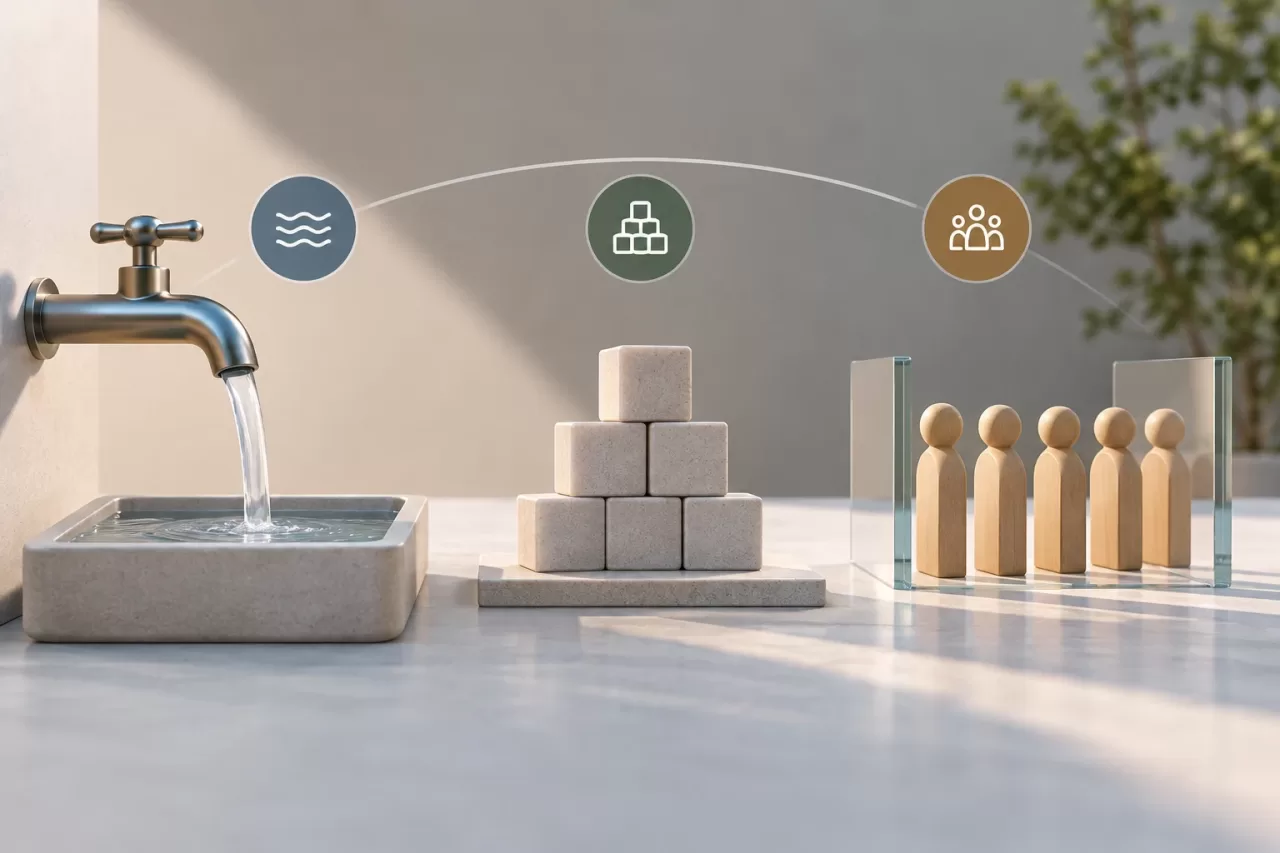
These controls address different problems and are not interchangeable:
- Request rate: limits how many requests are accepted within a short interval. It helps contain bursts or sustained traffic that overloads the application.
- Accumulated quota: limits total consumption over a longer period, such as a number of operations per day or billing cycle. It helps govern contracted usage or accumulated costly workloads.
- Concurrency: limits how many operations are running at the same time. It is useful when each operation can occupy workers, connections, or other resources for a long time.
A client can stay within a rate limit and still accumulate many long-running simultaneous operations; it can also make a small number of requests that consume a costly daily quota. Choose a control based on the risk you want to reduce and, if you need several, specify how they interact and which one is applied first.
Decide which identity and resource to limit
The limit key should represent a unit of consumption that makes operational sense. Depending on the product, it could be a credential, user, organization, client application, route, or a combination of these. Limiting only by IP address can penalize shared networks and does not distinguish authenticated consumers well; an IP address can serve as a complementary signal for anonymous traffic or security controls.
For authenticated clients, it is advisable to tie the policy to a stable identity and isolate organizations from one another. A credential shared by several systems can make it difficult to identify who is generating a burst: where possible, use separate credentials or add dimensions that allow consumption to be attributed. Avoid including untransformed secrets in counter keys or logs.
Not all routes have the same cost. A simple query and a large export should not necessarily consume the same budget. You can assign weights or different policies to costly operations, provided the criteria are understandable and consistent for consumers. Also review service limits: an API can receive few requests and still overload a shared dependency, such as a database or external provider.
Choose windows that reflect usage patterns
A fixed window is easy to explain, but it can allow a burst at the end of one interval followed by another at the beginning of the next. A sliding window reduces this effect at the cost of more storage and computation. A token system allows limited bursts while controlling the average rate; it is useful when legitimate traffic arrives in waves. The choice depends on the consumption pattern and the required level of precision.
Do not confuse a legitimate activity spike with abuse. Scheduled workloads, start-of-day synchronizations, or retries after an interruption can concentrate requests. If the product allows bursts, explicitly define their size and how long it takes the budget to recover. For long-running operations, also limit concurrency or apply admission control before scarce resources are occupied.
Client retries also matter. If a temporary response triggers immediate retries, the limit can make the spike worse. Recommend progressive backoff, ideally with jitter, and define whether repeated operations with the same idempotency key count as new requests or as a safe repeat.
Coordinate counters when PHP runs across multiple instances
A counter stored only in process memory can work on a single instance, but it loses consistency when traffic is distributed across several. Each server could accept part of the limit, exceeding it in aggregate. In deployments with multiple instances, state must be coordinated through shared storage or an equivalent mechanism with appropriate atomic operations.
Also design how the system behaves when the counter system fails. If it becomes unavailable, rejecting all requests can disrupt legitimate clients; accepting all requests can expose a critical dependency. The decision depends on the route’s risk: it may be reasonable to fail differently for a low-impact query than for an operation that incurs high costs. Document the criteria and alert on degraded behavior.
Avoid counter keys that are too general, mixing organizations or routes, as well as keys that are too fragmented, making it difficult to control total consumption. Define expiration and state cleanup so temporary keys do not accumulate indefinitely. Check that configuration changes do not unexpectedly reset or duplicate counters.
Make rejection part of the API contract
When a limit is reached, return an HTTP status consistent with the API contract—typically 429 Too Many Requests for rate limiting—and a structured body that identifies the type of limit without revealing internal information. If the operation is rejected for another reason, do not use this status misleadingly.
Include useful recovery guidance, such as the estimated time to retry or the limit and consumption details defined by the contract. If you send Retry-After, ensure it represents a valid wait time. Keep responses consistent across routes and avoid exposing other clients’ counters. Consumers must be able to distinguish a temporary rejection from authentication, validation, or availability errors.
Observe the impact and adjust based on evidence
Log accepted and rejected requests, the identity or client segment in a secure manner, the route, the policy applied, and the reason. Also measure latency, concurrency, and pressure on relevant dependencies. Do not store credentials or unnecessary personal data; use protected or aggregated identifiers when they are sufficient for analysis.
An increase in rejections does not by itself prove that the threshold is too strict. Look for patterns: affected clients, times, routes, operation duration, and subsequent retries. Investigate signs of false positives, such as rejections concentrated among organizations with shared credentials or scheduled tasks. Adjust one variable at a time and keep a way to roll back the change.
Roll out the policy gradually
Before enforcing a limit, evaluate the policy against usage data and test representative scenarios. If the architecture allows it, log which requests would have been rejected without blocking them; this observation does not replace load testing or guarantee that historical data will predict every spike.
- Define the risk you want to control and whether that calls for a rate limit, quota, concurrency limit, or combination.
- Assign limits by identity and resource, and verify isolation between users and organizations.
- Test bursts, slow operations, retries, shared credentials, and counter-store failures.
- Verify that multiple instances apply the limit in a coordinated manner and that temporary state is cleaned up.
- Validate the rejection response, retry guidance, and compatibility with current consumers.
- Monitor rejections, latency, and dependencies; communicate changes that could affect integrations.
Consumption limits in PHP APIs must protect both the platform and client continuity. The best policy is not the strictest one, but the one that controls risk with attributable rules, predictable responses, and enough evidence to correct unintended effects.