Bringing in external PHP professionals can increase delivery capacity, but distributing tickets by volume is not enough to keep work moving. An apparently self-contained task may depend on product decisions, permissions, domain knowledge, or changes to modules maintained by the internal team. If those dependencies are not made visible, delays, rework, and uncertainty about who should decide can arise.
The useful question is not how many tasks each team receives, but what each can complete with the decisions, access, and interfaces available. To determine how to divide tasks for an external PHP team, it helps to classify the work, define responsibilities, and agree on how to handle blockers before starting.
Why distributing tasks by volume creates hidden dependencies
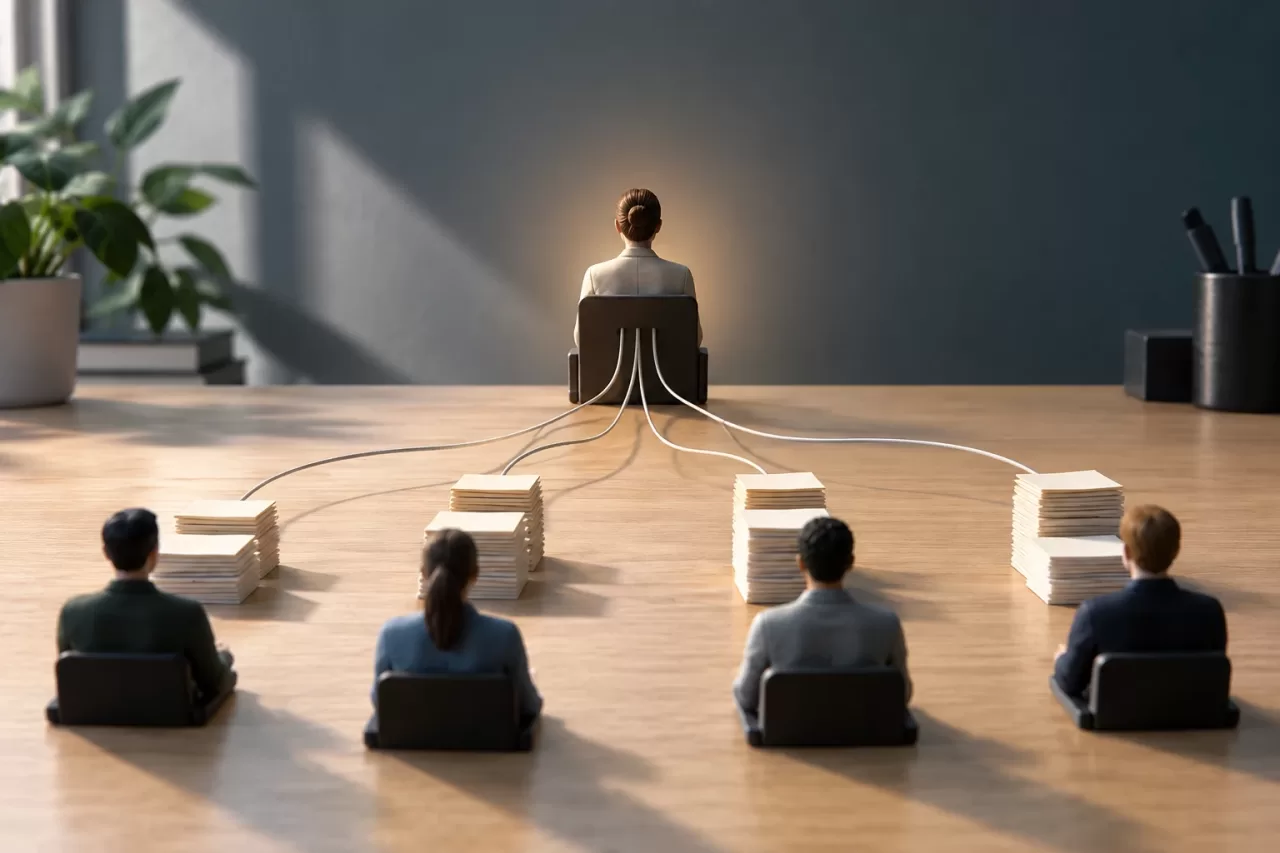
A balanced ticket list does not guarantee a balanced workload. An external team may receive several small tasks that, taken together, depend on the same internal person to clarify business rules or approve changes. In that case, the real capacity limit is not the number of developers, but the response time of the person with the necessary information or authority.
There are also technical dependencies that are difficult to spot in a ticket description: a shared database schema, an internal API without a stable contract, a deployment configuration managed by another team, or an undocumented security convention. If the external team discovers these requirements after starting, it may end up implementing an incompatible solution or waiting for access.
That is why, before assigning a work block, you should identify what decisions the implementer is authorized to make, which components they can modify, and which people or systems could prevent progress. Autonomy does not mean working without communication; it means being able to complete a defined scope without depending on ad hoc approvals at every step.
Inventory decisions, modules, access, and knowledge
For each work block, note the dependencies that could affect delivery. There is no need to create an exhaustive map of the entire PHP application: it is enough to understand the relationships relevant to that scope. Include at least the following:
- Decisions: business rules, expected behavior in error cases, and criteria requiring product or architecture approval.
- Modules and ownership: who maintains the components involved and whether the change could affect shared services.
- Interfaces: endpoints, events, data contracts, internal libraries, and response formats.
- Access and environments: repositories, test data, tracking tools, and the permissions needed to develop and validate.
- Knowledge: domain context, code conventions, and previous decisions that cannot be inferred from the implementation.
It is useful to distinguish known dependencies from unanswered questions. A task that requires a business decision is not fully ready if nobody is assigned to make that decision. Likewise, repository access does not mean appropriate access to sensitive data: the environment and test data must be agreed on in accordance with project policies.
Classify work as autonomous, collaborative, or internal
With the inventory in view, classify tasks according to their level of dependency. The category describes how to organize the work, not the importance of the person doing it.
- Autonomous: the scope and criteria are clear, the required interfaces are stable, and the external team has access and context. It can implement and test the work block, communicating progress and decisions within agreed boundaries.
- Collaborative: part of the work can be implemented, but shared decisions, coordination with other modules, or frequent reviews are required. Assign owners from both teams and establish synchronization points tied to specific decisions.
- Reserved for the internal team: the work requires authority over global priorities, knowledge that is difficult to transfer, management of critical credentials, or cross-cutting changes whose ownership is defined internally. This does not prevent the external team from contributing analysis or a narrowly scoped implementation.
The classification can change. If an interface is documented and stabilized, a collaborative work block may become autonomous. If analysis reveals a regulatory or product decision that still has no owner, it may be necessary to pause and reclassify the work rather than assume the risk.
Define responsibilities through deliverables and interfaces
A useful assignment describes the outcome and its boundaries, not just a list of files to modify. For example, the deliverable could be a PHP endpoint that complies with an agreed contract, along with automated tests and documentation of error cases. The description should also state what is outside the scope and who owns the related decisions.
When two teams work on connected components, specify the interface before dividing up the implementation. For an API, this may include authentication, parameters, response codes, validation, and compatibility. For an asynchronous process, it may include the message format, retries, and duplicate handling. The contract does not need to anticipate every internal detail, but it should reduce the number of decisions that would otherwise block integration.
Complete the assignment with observable acceptance criteria. Instead of saying “the change must work,” define what behavior should be seen in normal and error cases, which tests are expected, and what review is needed. Specify who accepts the result: the person who maintains the module, product, or both, depending on the type of decision. This separates implementation from the authority to approve business or architecture changes.
Agree on how to resolve dependencies and blockers
Blockers cannot be eliminated entirely; they become manageable when they are detected and have a path to resolution. Agree on what the external team should do if a decision, access, or response from another team is missing. For example: record the blocker along with its context and impact, assign it to an owner, and propose a safe alternative if one exists.
Set a channel and response time appropriate to the criticality of the work, without promising constant availability. Also define which priority changes can be made during the work block and who authorizes them. If a new request displaces the agreed scope, update the priority and acceptance criteria; do not add informal work and expect the schedule to remain unchanged.
For shared changes, agree on an integration strategy: branches and reviews, deployment order, temporary compatibility, or using a feature flag where appropriate. Deploying code is not the same as releasing or enabling a feature for users. If gradual exposure is needed, define who controls activation, how behavior is monitored, and how the feature is disabled if a problem occurs.
Review the task allocation after the first deliverables
Use the first deliverables to check whether the initial classification was correct. Autonomy is evident when the team completes the scope with few repeated clarifications, tests and reviews find the expected issues, and integration does not depend on last-minute interventions. It is not measured solely by coding speed: a fast delivery that creates rework or integration debt does not show that the allocation is working.
Signs of friction include several tasks waiting on the same internal person, repeated questions about rules that have already been agreed, reviews arriving after the work is complete, or changes crossing module boundaries without a clear decision. Look for specific causes: missing documentation, delayed permissions, unstable contracts, ambiguous criteria, or too many approvals. Adjust the process or scope before attributing the problem to a team's capacity.
Also review who retains knowledge and code ownership. Necessary documentation, tests, and a shared review help the internal team maintain the result. Collaboration should not mean that decisions remain implicit in private conversations or with a single person.
Short template for assigning a work block
Before starting each work block, complete a short form with these fields:
- Objective and outcome: what problem is being solved and what deliverable is expected.
- Owners: who implements, who decides, and who accepts the result.
- Scope and boundaries: what is included, what is excluded, and which components can be modified.
- Dependencies: decisions, access, contracts, people, and other work required.
- Acceptance criteria: verifiable behaviors, tests, and integration conditions.
- Blocker management: channel, owner responsible for resolving blockers, and how to communicate impact or alternatives.
- Classification and review: autonomous, collaborative, or internal; date or condition for reviewing whether the classification remains appropriate.
This form does not replace conversation between teams. It helps ensure that those conversations produce verifiable agreements before work is committed. When boundaries, decisions, and dependencies are explicit, it is easier to add external capacity without turning the internal team into a mandatory checkpoint for every change.