An AI response may appear accurate and still be unsuitable for operating on a system. Classifying a request as urgent, suggesting that a field be completed, or recommending that a workflow be started does not mean it has authorization, sufficient context, or complies with business rules. The risk arises when a textual or structured suggestion is turned into an executable command without independent safeguards.
To validate structured AI outputs in PHP, it is advisable to treat the model as a component that prepares proposals, not as an authority that modifies records, assigns owners, sends communications, or starts processes. The application retains the decision, applies its own rules, and records why a proposal was accepted, corrected, or rejected.
A plausible output is not a valid instruction
Models can return syntactically correct JSON and still include a nonexistent priority, an identifier that does not correspond to the customer, an impossible date, or an action the user is not allowed to request. They can also fill in data that is not present in the input, misinterpret an ambiguity, or follow an old format after a contract change.
The operational boundary must be explicit: AI can propose an action and explain the data it used; the system decides whether that proposal becomes a draft, requires review, or can be executed under very limited conditions. This separation protects both data integrity and decision accountability.
A good starting point is to classify each action by impact:
- Low impact: label a draft, suggest a category, or extract non-critical fields.
- Medium impact: create a pending task, propose an owner, or prepare a response for review.
- High impact: change contractual statuses, assign irreversible work, modify amounts, delete data, communicate externally, or activate sensitive processes.
Permissible autonomy does not depend on AI having a high stated confidence. It depends on reversibility, the cost of an error, the verifiable quality of the data, and the existence of controls outside the model.
Define a proposal contract before integrating the model
The output contract defines what the AI component can propose and what is outside its scope. It should be small, typed, and versioned. Instead of asking “decide what to do with this request,” specify a closed list of actions and the fields required for each one.
{
  "version": "1",
  "action": "create_task_draft",
  "category": "billing",
  "priority": "normal",
  "summary": "Review invoice discrepancy",
  "sourceReferences": ["message:123"],
  "confidence": 0.82
}
The action list should use controlled values, for example create_task_draft, request_more_information, or no_action. It is not advisable to accept method names, queries, code snippets, free-form recipients, or instructions such as “update the order.” The application translates an allowed action into a specific internal operation.
Fields, states, and evidence
In addition to types and permitted values, the contract must indicate which fields are required, which combinations are incompatible, and what evidence the proposal must provide. A category may be valid but require at least one reference to the source message or document. Confidence, if collected, is an auxiliary data point for prioritizing reviews; it does not replace validation.
Versioning the schema makes it possible to safely reject outputs from retired contracts. If a change adds a required field or removes an action, the adapter must recognize the version and avoid implicit interpretations.
Apply four safeguards before any effect
Validation must take place in separate layers. A failure in one layer is not offset by an apparently reasonable response in another.
- Format: check that the response can be decoded, complies with the expected schema, contains no unexpected critical fields, and that each value has the correct type. Invalid JSON, an unknown enumeration, or a missing required field are rejected.
- Domain: verify the application's own rules. For example, that the category exists, that the priority applies to the request type, that the referenced account is active, and that the source reference belongs to the processed context.
- Authorization: check what the actor who initiated the workflow can do and which permissions the operation requires. AI does not inherit unlimited privileges or decide the scope of access. The server applies the current identity, tenant, and policies.
- Operational conditions: review concurrency, current states, limits, dependencies, and idempotency. A valid proposal may not be executable if the case has already been closed, another process changed the record, or a load threshold has been exceeded.
Semantic validation must query internal sources of truth. It is not enough for the model to return a well-formed identifier: the repository or domain service must verify its existence, ownership, and status. Avoid having the model response carry authorization data that the application can resolve on its own.
PHP architecture: separate proposal, decision, and execution
A maintainable architecture separates responsibilities. The AI adapter prepares the request, applies size limits, and obtains an output; it does not write to the business database. A DTO represents the parsed proposal. The domain validator transforms that proposal into a decision with explicit errors. Finally, an authorized executor applies only approved decisions.
final class ActionProposal {
    public function __construct(
        public string $action,
        public string $category,
        public string $priority,
        public array $sourceReferences,
    ) {}
}

$proposal = $aiAdapter->propose($input);
$validation = $domainValidator->validate($proposal, $context);

if (!$validation->isApproved()) {
    $auditLog->recordRejected($proposal, $validation->reasons());
    return $validation;
}

return $decisionService->route($validation->approvedProposal(), $context);
The decision service can create a draft, place it in a review queue, or request human approval. The final executor must receive an internal decision object, not the raw response or the AI JSON. This prevents an accidental expansion of the contract from becoming a new operational capability.
Use transactions for related changes, idempotency keys for retries, and concurrency controls when multiple people or processes can act on the same case. Also distinguish deployment from activation: code can be deployed without exposing the workflow to real users. Gradual activation makes it possible to observe rejections, timings, and corrections before expanding the scope.
Choose human review, limited automation, or rejection
Human review is appropriate when there is material ambiguity, sensitive data, external consequences, policy exceptions, or high correction costs. The review interface should display the proposal, the permitted source evidence, the rules passed, and the reasons for alert, without presenting the recommendation as a fact.
Limited automation may be reasonable for reversible, bounded operations: creating an unassigned draft, applying a provisional label, or routing a request to a general queue. It must have frequency limits, the ability to undo, and subsequent oversight. If data is missing, rules conflict, or the action is outside the allowed list, the safe behavior is to reject or escalate, not improvise.
Before using AI, evaluate a deterministic alternative. If inputs follow stable patterns, rules, guided forms, selection lists, or a conventional classifier may be cheaper, auditable, and more predictable. When AI is used, define the use case, a representative evaluation set, operational thresholds, cost by volume, and a fallback mode if the provider fails or exceeds the expected time.
Example: turning a request into a task draft
Suppose an incoming request mentions an invoice discrepancy. AI can propose the billing category, normal priority, and a task summary. The validator checks that the message belongs to the current tenant, that the category is enabled, and that there is not already an open case with the same reference. If everything is correct, the system creates a draft without assigning an owner or modifying the invoice status.
An operator reviews the draft, confirms or corrects the category, and decides the assignment according to the current workload and permissions. This distinction prevents a plausible inference about an owner or an amount from becoming an incorrect modification. If the contract requires an invoice number and it does not appear in the message, the proposal must request additional information, not invent it.
Traceability, privacy, and testing before expanding the workflow
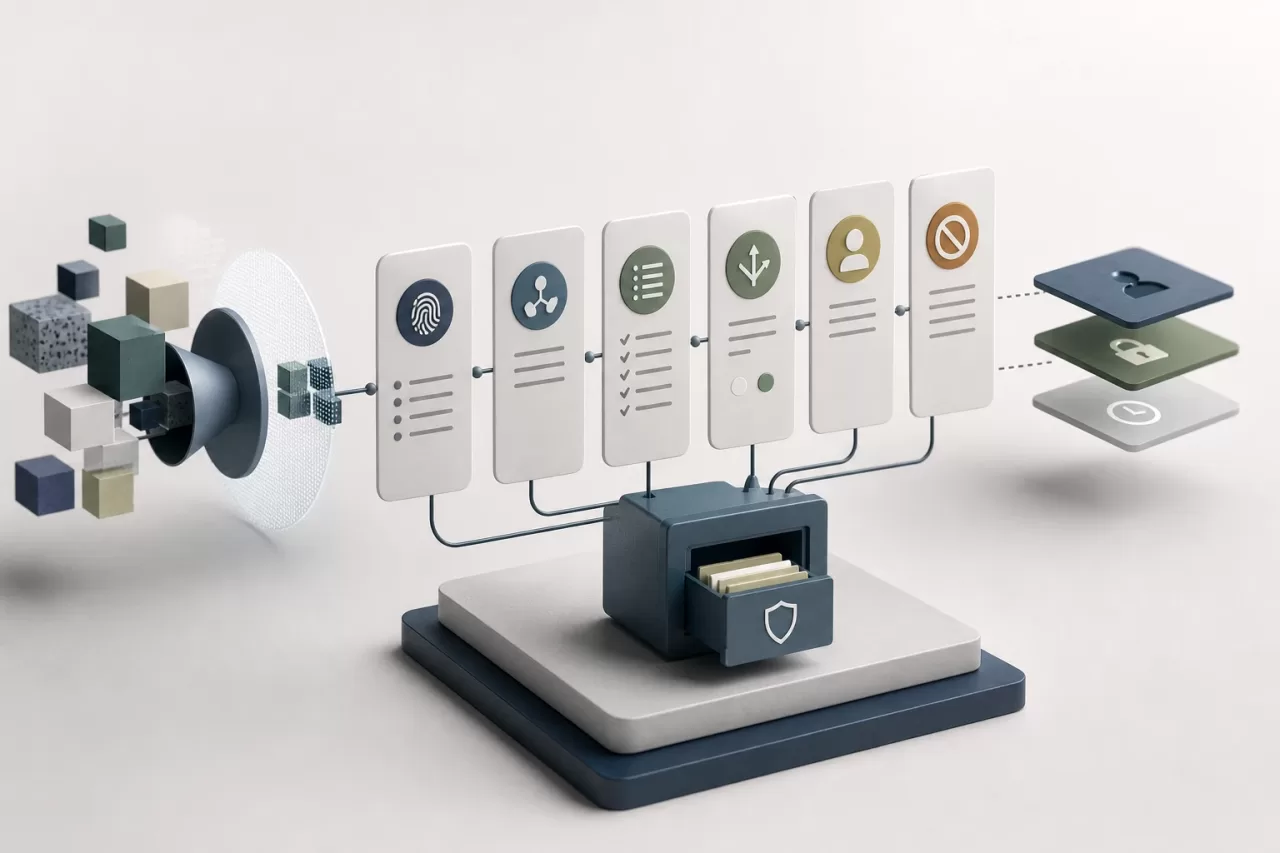
Record a correlation identifier, contract version, fingerprint or reference of the minimized input, normalized proposal, results of each validation, final decision, approving actor when applicable, and rejection reason. The log must be useful for investigating incidents without duplicating unnecessary personal data or sensitive content. Apply retention, restricted access, and minimization techniques appropriate to the process risk.
Test the workflow with representative and adversarial cases: incomplete inputs, contradictory instructions, invented values, references from another tenant, concurrent state changes, responses in an old format, latency, and AI service unavailability. Acceptance criteria must measure whether unauthorized operations are blocked, whether drafts are recoverable, whether rejections are understandable, and whether the system maintains a functional alternative in the event of failures.
Safe operation is not about making the model respond every time. It is about ensuring that, when it responds incorrectly, takes too long, or does not respond, the PHP application retains control and does not produce effects it cannot justify.