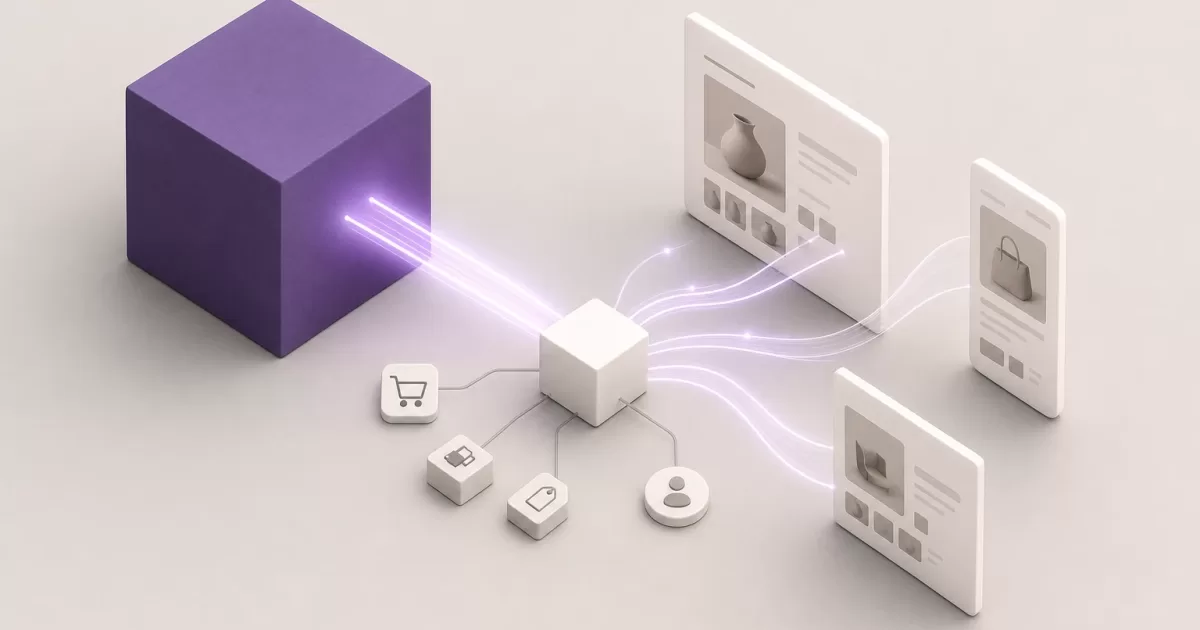
Headless WooCommerce consists of separating the interface the shopper sees from the system that manages the store. The frontend can be an independent web application, an experience for multiple channels, or a layer specific to a campaign. WooCommerce, meanwhile, retains the back office and some or all of the commerce logic.
Separation does not by itself solve performance, conversion, or content issues. It can improve design freedom and the delivery of specific experiences, but it also introduces API contracts, state synchronization, a new security surface, and more points of failure. The useful question is not whether a decoupled architecture is more modern, but which specific limitation of the current theme it resolves and what operational cost it adds.
When a decoupled frontend makes sense
A conventional WooCommerce theme is usually the most efficient option when the catalog, product pages, content, and checkout follow familiar patterns. It allows the team to edit, publish, and test within a single environment. Changing architecture solely to achieve a different visual interface is rarely worthwhile.
There are stronger signals for considering a separate frontend:
- The shopping experience must coexist with an application, a complex configurator, or navigation that the theme and its extensions cannot clearly support.
- The business needs to serve the same catalog to several touchpoints, such as a public website, a private area, or an application, without manually rebuilding the data in each one.
- Content pages require deployment cadences, components, or performance that are clearly different from those of the current storefront.
- There are integration requirements that make a dedicated experience layer necessary, for example with external search, governed personalization, or internal services.
- The team has the capacity to maintain the frontend, integration, end-to-end testing, monitoring, and incident management across systems.
Conversely, it is advisable to retain the theme or improve its implementation if the problem is a slow template, unoptimized images, too many plugins, inefficient queries, or poor cache configuration. A decoupled frontend does not automatically correct these causes and can hide them behind a more complex API.
A single source of truth for commerce operations
The central rule is simple: separating presentation must not create a second commerce engine. WooCommerce must remain the authority, unless a responsibility is explicitly replaced by another system and the entire operation is redesigned.
At a minimum, the owner of each domain must be identified: catalog, variations, prices, taxes, stock, coupons, promotions, customers, orders, refunds, and shipping statuses. If WooCommerce calculates a price based on country, shipping method, customer role, or coupon, the frontend should not replicate that formula. It must request the result from the authorized commerce flow and display it.
This is especially important with extensions. A promotion may depend on a rule installed in WooCommerce, and an apparently simple price may incorporate taxes, rounding, currency, or cart discounts. Reimplementing these rules in JavaScript or in a parallel service creates divergences: the shopper sees one amount and the order records another.
The frontend can present, organize, and guide the purchase decision; the commerce system must validate and calculate the transaction.
Reference architecture and API boundaries
A sensible architecture separates responsibilities without assuming that all information must be public. The frontend consumes a deliberately designed API. WooCommerce and WordPress manage administration, content, and commerce. An integration layer, when needed, normalizes responses, applies authorization, and avoids exposing internal details of plugins or personal data.
Reads, writes, and events
Catalog, category, and content reads can be served through experience-oriented endpoints. They should include only the necessary fields: stable identifiers, displayable availability, images, attributes, prices with their context, and invalidation references. Administrative metadata should not be returned merely for convenience.
Writes require another level of control. Adding an item to the cart, applying a coupon, choosing shipping, initiating payment, or creating an order are actions that must go through session validation, permissions, abuse limits, and current rules. The price, discount, tax, stock, or total submitted by the browser must never be trusted. The server must recalculate them before confirming the operation.
Webhooks or events are useful for communicating order, payment, stock, or return changes to other systems. They must be verified, idempotent, and log retries. The same event may arrive more than once; the consumer needs a deduplication key and must not create two irreversible actions because of a repeat.
Session, cart, and payment
The cart is where many headless projects discover their real complexity. You must define how the visitor is identified, how their session is preserved across domains or subdomains, what happens when they sign in, and how an anonymous cart is merged with an existing one. Cookie restrictions, CORS, and protection against forged requests must be part of the design, not final adjustments.
Checkout also depends on payment gateways, redirects, strong customer authentication, and possible additional fields. Before building it outside WooCommerce, you must verify which APIs and flows the specific gateway supports. A cart demonstration does not prove that payment, the return from the provider, order creation, and reconciliation work operationally.
A prudent alternative is to decouple content, navigation, or product pages while temporarily retaining the checkout hosted by the store. This reduces the initial scope, although it requires a clear transition and visual consistency.
Performance, SEO, and up-to-date commerce data
A fast frontend can display outdated prices or availability if the caching strategy does not distinguish editorial content from commerce data. Category and product pages can be cached, but they need to be invalidated or revalidated when a price, variation, relevant stock level, or promotion changes. Cart and checkout responses, by contrast, are usually private and session-dependent.
Define which event invalidates each representation and how much delay is acceptable. Updating an editorial description is not the same as removing an out-of-stock product. When freshness cannot be guaranteed on a cached product page, the frontend must query the current status before allowing the purchase and communicate any change clearly.
For SEO, rendering must deliver titles, descriptions, indexable content, canonical URLs, and structured data consistent with the actual product. The migration must preserve redirects, pagination, indexable filters, and exclusion rules. Having two active frontends without a policy for canonical URLs and routing can create duplicate content.
Operations and diagnosis across teams
The architecture must be manageable by those who publish content, handle orders, and resolve incidents. Document where each element is edited, how long it takes to publish, and which system takes precedence if there is a discrepancy. If an agent modifies an order or issues a refund in WooCommerce, the systems displaying that order must receive and process the change in a traceable manner.
Observability must connect the frontend request with the API call, cart, payment attempt, and final order. Use correlation IDs, logs without sensitive data, error metrics, and alerts for webhook failures or dependency degradation. An incident must be able to answer specific questions: was the price calculated at the source? Did the gateway confirm payment? Was the order created only once? What response did the customer receive?
Phased adoption and exit criteria
It is not necessary to replace the entire store in a single launch. Start with a high-value, low-risk section: a campaign landing page, editorial content connected to the catalog, or a product family without exceptional rules. Maintain rollback paths and measure operational errors, not only page load speed.
Before expanding the scope, test the journeys that support the business both automatically and manually:
- Variations, context-based prices, taxes, coupons, shipping, and rounding.
- Low stock, out-of-stock items, reservations, and concurrency when completing purchases.
- Anonymous cart, sign-in, session recovery, and sign-out.
- Approved, canceled, pending, repeated payments and incomplete return from the gateway.
- API permissions, abuse, modification of amounts from the client, and exposure of personal data.
- Cache invalidation after changes to prices, stock, content, and promotions.
- Failure of the frontend, API, or an external service, including the available purchase alternative.
The exit should not be based solely on the interface appearing finished. There must be verifiable consistency between what is displayed, what is charged, and what the team can operate. This makes headless WooCommerce a controlled product and architecture decision, rather than a costly duplication of the store.