Automating an operation does not always mean executing it without human involvement. If an action could alter important data, apply a business condition, move funds, or affect third parties, it may need to wait for a person to authorize it. A human approval workflow in PHP automation provides this control without turning the process into an informal chain of messages and decisions that are difficult to reconstruct.
The key is not to add an “approve” button, but to define what is being proposed, who can decide, what information they are deciding on, how long the decision remains valid, and what happens next. The system must be able to explain every state and prevent an old or duplicate approval from executing an action different from the one that was reviewed.
Decide when to pause an operation
A review after the fact helps detect problems after an action has occurred. Prior approval, by contrast, stops execution until a decision is received. Require authorization when the potential impact, difficulty of reversing the action, or uncertainty exceeds the level accepted for automation.
Assess each operation using specific questions: Could it change data that is difficult to recover? Does it affect money, rights, access, or commitments to customers? Is there a verifiable rule that would allow it to run autonomously? How much damage could an error cause, and how much time is available to respond? A routine, reversible, and limited operation could run automatically and be recorded for review. An exceptional or high-impact action may require authorization before execution.
Avoid applying human approval to everything by default. An overloaded queue causes delays and encourages rubber-stamping. Define thresholds and exceptions, and measure pending items, wait times, rejections, and expirations to identify rules that may need adjustment. The decision should be based on actual risk, not merely on whether an operation is technically possible.
Define what is proposed and what can be authorized
The reviewer needs to understand the effect of the operation, not decipher an internal PHP object. Show the current and proposed values, the reason, the data source, relevant consequences, and any limitations. If the decision depends on a rule, provide the explanation needed to apply it. Hide or protect personal data that is not required.
Separate the proposal command from the authorization. The proposal describes the action and its parameters; the authorization permits that specific proposal to be executed. It must not grant general permissions or allow the approver to silently edit the parameters. If changes are needed, the reviewer can request a modification; the system creates an updated proposal that must pass the applicable authorization rules.
Apply the principle of least privilege: restrict who can create, authorize, reject, or cancel proposals, and check those permissions on the server at every transition. When the risk warrants it, require that the proposer cannot authorize their own operation. This separation must be implemented in the permission logic, not rely solely on hiding buttons in the interface.
Model explicit states and transitions
Represent the process as a state machine. A useful initial set might include pending, approved, executing, rejected, changes_requested, expired, cancelled, and executed. A pending proposal can be approved, rejected, cancelled, or expire; an approved proposal can proceed to execution only if it is still valid; an operation being executed can finish as executed or return to a recoverable state if it is determined to have had no effect. An executed proposal cannot be approved again.
Store the current state alongside an immutable history of decisions and transitions. Record the proposal ID, previous and new states, actor, date and time, reason, and a reference to the version of the data that was reviewed. Do not replace the history when updating the record: it is needed to audit what happened and diagnose failures.
In PHP, centralize transitions in a domain service or equivalent component. Avoid having different controllers change state directly through generic updates. Validate the transition and permissions within a transaction where appropriate, and reject actions that are incompatible with the current state. This structure reduces concurrency errors and makes it easier to test the rules without depending on the interface.
Prevent stale approvals and duplicate executions
Data can change while a proposal is waiting. A person must not authorize a condition that no longer matches the operation about to be executed. When creating the proposal, store a version, update timestamp, or fingerprint of the relevant fields. When it is approved, check it again against the current state.
Checking at approval time is not enough: the data could still change before the operation is applied. Immediately before execution, compare the current version or fingerprint with the approved one again. If they differ, stop the process, invalidate the authorization for that proposal, and request a new decision based on the updated data. Depending on the risk, you can show the differences and require explicit confirmation, but do not automatically reuse the previous approval.
An expiration limits how long a decision is considered valid. When it expires, mark the proposal as expired and require new authorization to continue. Every retry must check that the authorization is still valid; never reuse an expired authorization to resume or repeat execution.
Approval must refer to an identifiable proposal and must not be a reusable signal. To prevent two concurrent workers from executing the same proposal, atomically claim or lock its transition from approved to executing: only one worker can claim it if the proposal is still approved and valid. As part of this local safeguard, also check idempotency and record the unique operation ID before proceeding. This prevents duplicates within the system, but a database transaction alone does not guarantee that an external API will apply an effect only once.
If the action takes place in another service, use an idempotency key that the service accepts and processes idempotently, if available. Record the correlation ID, attempt, and responses. If the response is lost or the outcome is unknown, do not blindly repeat the effect: check the remote status using that ID or reconcile the outcome against reliable data. If it is not possible to confirm whether the effect occurred, stop further automatic attempts and escalate the case to an operator. A known failure before the request is sent may allow a retry, provided that the state and authorization are checked again.
If a worker fails and leaves a proposal in executing, do not automatically mark it as executed or resend it without diagnosis. A recovery process must determine whether the effect occurred, using the local record and, where appropriate, querying the remote service. If it confirms that the effect did not occur, it may return the proposal to an executable state only after revalidating its validity, data, and authorization; if the outcome remains unknown, it must keep the proposal blocked and escalate it.
Design an operational queue and a manual fallback
The queue should make it possible to find pending items by age, impact, owner, and expiration date, while also showing the context behind the decision. Explain why a case is blocked and what action is appropriate: wait, request changes, cancel, or escalate. The interface should also make clear what will happen upon approval, rather than merely offering decision buttons.
Define a fallback for when a dependency fails, such as the notification service or an integration required to execute the action. The proposal can remain pending while a controlled procedure allows an authorized person to review the case in the available operating environment. The manual path must enforce the same checks, record the actor and reason, prevent parallel execution, and reconcile the outcome when the integration is restored.
Do not turn a technical outage into implicit approval. If identity, permissions, or required information cannot be verified, the system must fail safely: pause, notify, and escalate. Define who can unblock the process, how that intervention is documented, and which tasks must be reviewed when service is restored.
Test the workflow and monitor its operation
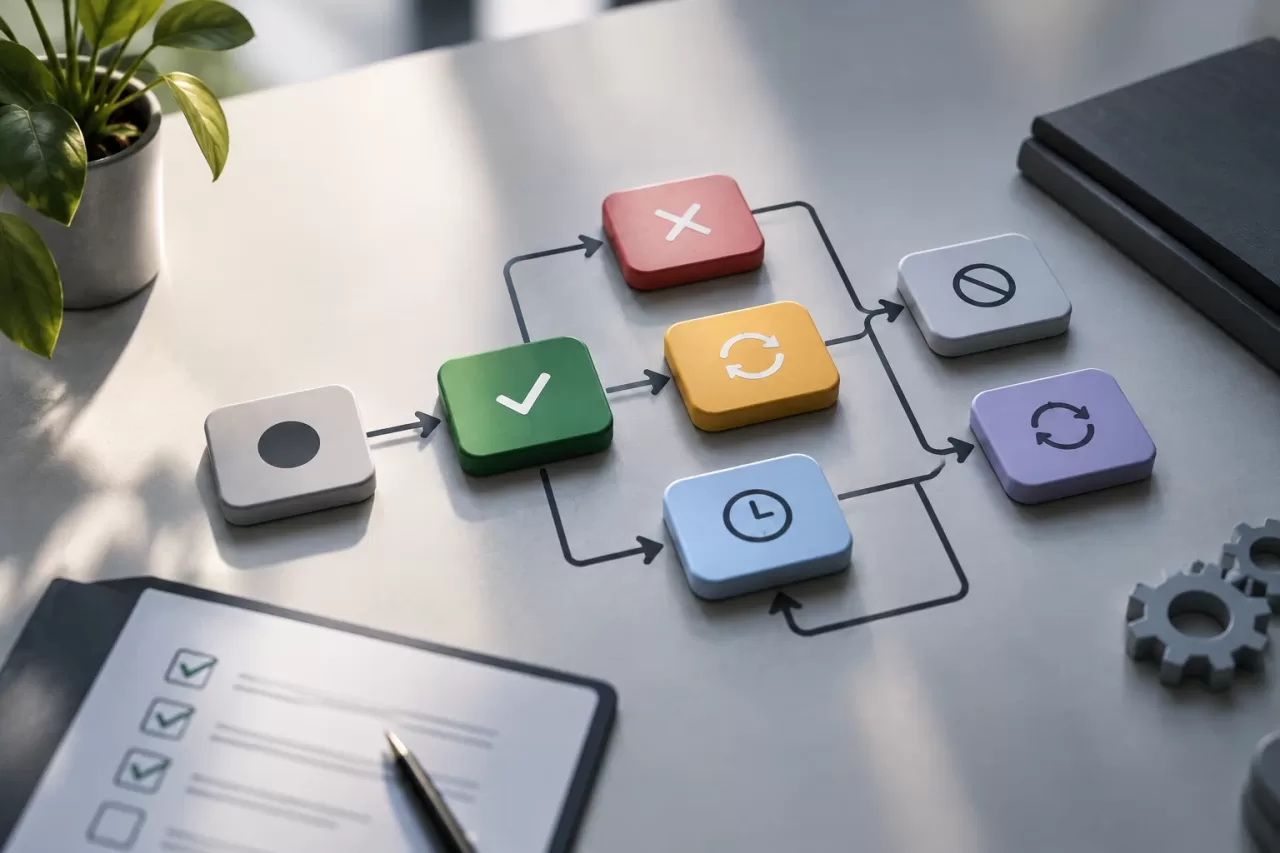
Test the domain rules and complete paths: approval, rejection, change requests, expiration, cancellation, and retries. Add permission tests to confirm that someone without authorization cannot change the state, and concurrency tests to ensure that two simultaneous decisions do not result in two executions.
Include cases where data changes while waiting or just before execution, remote execution fails after accepting the request, and a response is lost even though the effect occurred. Verify that atomic claiming allows only one worker to execute the proposal, that retries reject expired authorizations, and that every manual intervention leaves an adequate record. In production, monitor the volume and age of pending items, expirations, execution errors, and cases requiring reconciliation.
A well-designed workflow maintains human oversight where it provides control, without leaving security to team members’ memory. Explicit states, separation of permissions, current reviewed data, idempotent execution, and a clear failure path turn an informal approval into a verifiable process.