Changing the email provider in a PHP application is not just a matter of replacing one set of credentials with another. The transport can change how senders, attachments, templates, sending limits, and error responses are configured. If the application mixes these decisions with business logic, the migration can generate duplicate messages, confusing statuses, or notifications that stop being sent without a clear signal.
The practical goal is for the application to decide what to communicate and for the provider to handle how to transport the message. This separation makes it possible to test the new service, retain operational references, and define a cutover with verifiable criteria. It cannot guarantee that an email will reach the inbox: acceptance by the external service is not the same as delivery, reading, or freedom from subsequent filtering.
Inventory messages before changing the integration
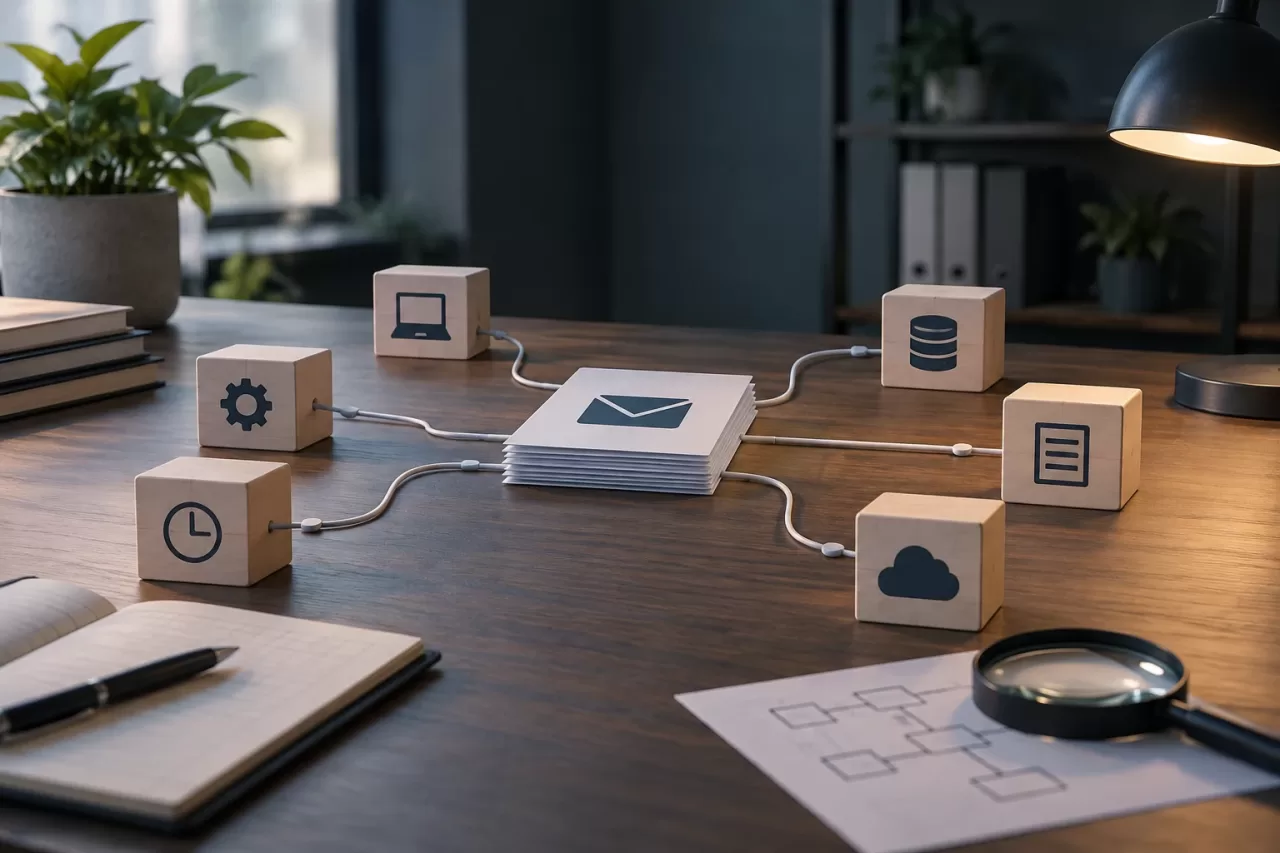
Start by identifying all email flows, not just the ones the team remembers. Search the code for transport calls and review background jobs, scheduled commands, administrative processes, and external services that may invoke the application. Cross-check your findings against the configuration and available logs.
For each message type, record:
- Origin and purpose: which operation generates it and what it is intended to achieve, such as confirming an action or reporting an incident.
- Priority and deadline: whether it must be processed immediately or can wait for an asynchronous job.
- Recipients and required data: who receives it and what information is needed to build the message.
- Format and constraints: plain text, HTML, attachments, sender, reply-to, and formatting or size requirements.
- Failure behavior: whether it is retried, left pending, escalated to a person, or canceled.
This classification prevents a critical notification from being treated like an informational message. It also reveals dependencies that can remain hidden during a transition, such as a template that uses data that has already been deleted or a job that retries indefinitely.
Separate business decisions from transport
Business logic should express an intent, such as requesting that a confirmation be sent. It should not know the details of an external API or build provider-specific headers. Define an internal contract that matches the application’s actual needs and place the concrete integration behind an adapter.
In PHP, a small interface can make this boundary explicit:
interface MailTransport
{
    public function send(OutboundMessage $message): TransportResult;
}
OutboundMessage can represent the sender, recipients, subject, content, and permitted metadata. TransportResult should distinguish, at a minimum, acceptance by the transport from a known error. Avoid calling a message “delivered” just because the request was accepted: the status should describe what is actually known.
The adapter converts the internal contract into the format required by the chosen service. Configuration—credentials, sender, endpoint, and options—should be kept outside the code and managed per environment, with secrets protected. If there are multiple providers, select the adapter through clear configuration rather than conditionals scattered throughout the business logic. Keep templates and notification policy separate from transport unless there is a specific reason to delegate their management.
An interface does not eliminate all differences between services. Size limits, attachments, error codes, and advanced features may not be equivalent. Document which capabilities are common and which are provider-specific; decide whether an exclusive feature is essential or should be adapted before the change.
Preserve statuses and useful references
Traceability should connect the send request to the operation that initiated it without turning the logs into a copy of the email. Assign an internal identifier to the message and retain a reference to the originating entity or event, such as an invoice or request ID. If the provider returns a message identifier, store it as an associated external reference, not as a replacement for the internal identifier.
Record transitions that help answer operational questions: when the send was requested, when it was attempted, how many attempts were made, what result the adapter reported, and whether a subsequent response is available. Define statuses precisely, for example, pending, accepted by the transport, rejected, and temporary failure. Do not invent a delivery status unless you receive a verifiable signal to support it.
Limit the data you log. Full content, attachments, addresses, and personal data can be sensitive and are not usually necessary to diagnose a transport failure. Store error codes and messages carefully, control access, and establish a retention policy. If external events or webhooks are received, validate their authenticity and avoid processing the same notification repeatedly.
Test the new service without duplicating real messages
Before cutover, validate the configuration in a controlled environment: credentials, authorized sender, formats, attachments, and error handling. Test representative flows from each inventory category, including temporary failures, rejection responses, and recovery of pending jobs. Check that logs retain internal references and that errors do not expose secrets.
Parallel testing requires special care. If the same event is sent to both providers with real recipients, you may generate duplicates. Instead, compare the message-building result without sending a second message, use a controlled test destination, or validate the request against a test environment when the service allows it. Do not assume that test mode reproduces all production conditions.
If real sending is being compared, define in advance which messages are included, who may receive them, and how an operation will be prevented from repeating. An idempotency key can help identify repeated requests if the application and transport support it, but it does not replace queue design or, by itself, guarantee that duplicates will not occur. Also review whether the old and new providers apply different limits or policies.
Set cutover and rollback criteria
Cutover should be a decision based on observable signals, not merely on whether the application has started. Agree on which flows will be activated first, who authorizes each step, and which indicators will be reviewed: connection errors, rejections, the age of pending messages, job duration, and available external responses. Set thresholds appropriate to the volume and risk level of each flow, without confusing acceptance with delivery.
Define in advance how to return to the previous transport. Temporarily retain its configuration securely and verify that the application version can select it. Determine what to do with messages queued during the change: pause and resume them, keep only one active route, or classify them before retrying. Changing providers does not cancel a send that the previous system has already accepted; blindly resending it can duplicate the message.
Rollback also cannot retrieve an email that has already been sent or undo a recipient’s decision or an external system’s action. It should be limited to restoring an operable sending route and processing whatever remains pending according to explicit rules. Retain transition logs so you can explain which requests were accepted, which failed, and which require review.
Transition checklist
- Inventory message types, origins, priority, recipients, and dependencies.
- Define the internal contract, adapter, and per-environment configuration.
- Assign internal identifiers and describe statuses without implying delivery guarantees.
- Review privacy, access, retention, and log contents.
- Test formats, errors, retries, and representative jobs without duplicating messages to real recipients.
- Establish owners, progress signals, cutover conditions, and a rollback procedure.
- Monitor the first sends and remove the old integration only when there are no remaining dependencies or pending messages that require its attention.
The migration is under control when the team can explain which message was requested, which attempts were made, what each transport confirmed, and what remains unknown. That clarity, combined with a small technical boundary and a tested cutover plan, reduces the risk of changing providers without attributing to the application guarantees that depend on external systems.